TECHNOLOGY
Why Loyalty Software is the New Growth Engine for Manufacturers

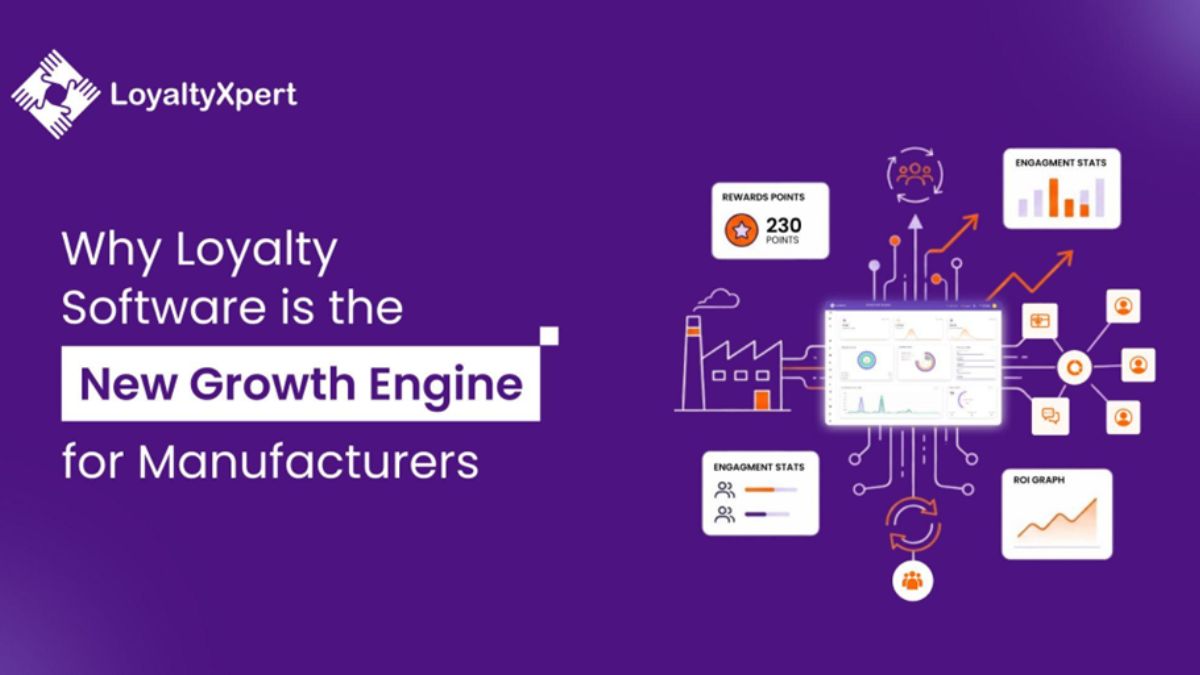
Manufacturers today operate in highly competitive, fragmented channel ecosystems. Distributors, dealers, and retailers have far more choices than ever, making long-term engagement harder to sustain. In this environment, competing solely on price is not enough to drive repeat business or channel loyalty.
As manufacturers focus more on relationship-driven growth strategies, loyalty program software is emerging as a really important tool for strengthening partner engagement and improving retention, resulting in more predictable revenue.
Instead of treating each and every sale as an isolated transaction, the manufacturers are investing more in long-term channel engagement strategies. The main focus is on repeat ordering behavior, distributor advocacy, and stronger partner alignment. This is where loyalty platforms help transform broken engagement efforts into well-structured, scalable growth programs.
By building proper channel relationships through data-driven engagement and incentive systems, the manufacturers can create more consistent participation across their partner networks while improving the long-term business stability.
Expanding Loyalty Software Role in the Manufacturing Ecosystem
The new loyalty platforms are not just limited to managing rewards & incentives. They now serve as centralized engagement systems that connect everyone, including distributors, dealers, retailers, and influencers, across the entire manufacturing ecosystem. Within this structure, channel incentive programs are used to shape specific partner behaviors across the distribution network, aligning sales activity, order frequency, and product focus with defined growth objectives. Every single interaction, purchase activity, and engagement milestone can be properly tracked, measured, and rewarded through a well-structured digital framework.
This properly structured approach gives manufacturers more visibility into partner participation, purchasing behavior, and engagement trends across indirect sales networks. Instead of relying on old, disconnected spreadsheets or manual follow-ups, businesses gain a more scalable, data-driven engagement model. As a result, manufacturers actually gain operational and engagement advantages across their whole channel networks.
With the correct loyalty software for manufacturers, loyalty is no longer just manual. It becomes a full system that drives real growth.
Image:
Title: Loyalty Software in the Manufacturing Ecosystem
Top text:
From Fragmented Network → Connected Ecosystem
A simple hub-and-spoke diagram
- Center circle:
💻 “Loyalty Software” - Connected nodes around it:
🏭 Manufacturer
🚚 Distributor
🏬 Dealer
🧑💼 Influencer / Retailer
(All connected with lines to the center)
Text under the diagram:
✔️ Tracks purchases & partner activity
✔️ Automates rewards & incentives
✔️ Supports multi-level engagement
Bottom text
“Turns manual loyalty into a growth system
Key Challenges Manufacturers Face in Channel Engagement
Without any framework, partners lose interest. They jump to other brands. They go for immediate advantages. This is where the problem actually lies. Many organizations still rely on outdated manual processes to manage partner engagement. Over time, these gaps can create broader channel engagement and performance issues, such as:
- Not able to measure the performance of partners
- Low engagement in channel loyalty programs
- Lack of a uniform reward program
- Minimal use of loyalty management software
This is precisely why Loyalty Program Software is critical.
How Loyalty Software Strengthens Dealer and Distributor Relationships
You recognize your distributor one time. Not following up. Not engaging. Eventually, you lose touch. This is a common problem. And this is where loyalty program software makes all the difference.
It establishes an endless cycle of engagement. Dealers earn points. Distributors monitor their progress. Everyone feels engaged. With well-organized channel loyalty programs, relationships are not based on temporary gimmicks anymore. They have sustainability and other advantages, such as:
- Rewards on every sale
- Clarity for your partners
- Constant communication and updates
Through Loyalty Software for Manufacturers, businesses transform passive partners into active participants. What’s the outcome? Trust, alignment, and sustainable relationships.
Strategic Business Benefits of Loyalty Platforms for Manufacturers
Manufacturers today face growing pressure from fluctuating demand, channel competition, and inconsistent partner engagement. Loyalty program software helps solve these challenges by creating a structured ecosystem that motivates distributors, dealers, and retailers to stay actively engaged with the brand. Instead of relying solely on pricing strategies or short-term schemes, manufacturers can build long-term channel loyalty through measurable, data-driven engagement programs.
A well-designed loyalty platform delivers more than repeat purchases. It improves visibility across the sales channel and helps manufacturers identify which partners contribute the most value. This allows businesses to segment partners, personalize incentives, and allocate budgets more effectively. Over time, these insights support smarter forecasting, better inventory planning, and improved sales predictability.
Loyalty platforms also strengthen channel communication. Manufacturers can use them to launch targeted campaigns, introduce new products, share training materials, and reward desired behaviors in real time. This creates a more connected channel ecosystem where partners remain consistently informed and motivated.
Another major advantage is operational efficiency. Manual reward tracking, claim validation, and partner communication often consume significant time and resources. Loyalty management software automates these processes, reducing administrative overhead while improving accuracy and transparency for channel partners.
Key strategic benefits include:
- Improved channel partner engagement and participation
- Better visibility into partner performance and buying behavior
- More accurate sales forecasting through data-driven insights
- Faster adoption of new products and promotional campaigns
- Reduced dependency on discounts as the primary sales driver
- Streamlined reward management and operational automation
- Stronger long-term relationships with distributors and retailers
Manufacturers can avoid fragmented engagement efforts with loyalty platforms. These platforms support scalable channel growth. They improve performance, transparency, and long-term business value.
Key Capabilities Manufacturers Should Prioritize in a Loyalty Platform
As channel ecosystems become increasingly complex, manufacturers require loyalty platforms that are scalable, easy to manage, and adaptable to different partner structures. The effectiveness of a loyalty system doesn’t depend only on rewards management. It also depends on how efficiently it supports the engagement and visibility with operational execution across the channel network.
The right platform should support evolving distributor and dealer ecosystems while integrating smoothly with existing business processes. It should simplify engagement management for internal teams while providing a frictionless experience for channel partners. The most effective loyalty platforms typically include capabilities such as:
- Quick and easy partner sign-up
- Reward automation and tracking
- Mobile-optimized platform
- Real-time reporting and insights
- Flexible program configuration
Ultimately, the most effective loyalty platforms balance operational simplicity with strategic scalability, enabling manufacturers to manage partner engagement efficiently while supporting long-term channel growth.
Putting It Together
An effective loyalty program is not just about rewards. It is about creating a structured and consistent engagement strategy that strengthens long-term business relationships. With the right loyalty program management software, businesses can streamline operations, improve partner participation, and scale their programs more efficiently.
Platforms like LoyaltyXpert help organizations manage and optimize loyalty initiatives through automation, tracking, and personalized engagement. A well-managed loyalty program ultimately supports stronger retention, better partner relationships, and sustainable business growth.
If you want to find out how this will help your company, you can request a demo or contact us.
Ask a room of technology leaders whether their mobile app is secure and most will say yes. Ask whether it is harder to secure than it was three years ago and the answer changes. The app itself has not become weaker. The environment around it has become more complicated, and the pace of business has quietly outrun the way most apps were originally designed.
That gap shows up first at scale. An app built for one product line, one payment provider and a few thousand users is a manageable thing to protect. The same app three years later may carry loyalty data, connect to a warehouse system, run on both iOS and Android against a shared backend, and absorb traffic peaks it was never sized for. Companies investing in custom mobile app development services tend to arrive at the same conclusion: security debt is usually architecture debt wearing a different name.
The pressure is not only technical. Regulators expect more, customers expect more, and enterprise buyers now raise security questions during procurement that used to appear only after the contract was signed. A weak mobile app is no longer just a line item on a risk register. It is a reason a deal stalls.
A second pressure arrived more quietly. Apps now talk to more systems than ever, and a growing number of those systems are intelligent. Teams adding recommendation engines, fraud scoring or document processing through custom AI software development services are also adding new data paths, new third-party dependencies and new decisions that must be explainable. Every connection is a door, and doors work best when they are designed rather than discovered.
What Enterprise Grade Actually Means for a Mobile App
“Enterprise grade” gets used loosely. In practice it describes five properties that hold up under pressure.
Scalability. An app is scalable when growth changes the numbers, not the design. If doubling your user base forces an emergency rewrite of authentication or session handling, you do not have a scaling plan. You have a postponed problem.
Security. Genuine security is layered: encrypted data at rest and in transit, sensible token lifetimes, protected local storage, hardened APIs and controlled third-party SDKs. Most incidents trace back to something ordinary rather than something exotic.
Performance. Slow apps get abandoned, and abandoned apps get replaced by unofficial tools that nobody governs. Performance is a security concern as much as an experience one.
Reliability. Uptime, graceful failure and predictable recovery matter more as the app becomes your primary channel. Systems that fail loudly are safer than systems that fail quietly.
Integration. Modern apps are hubs. They connect to CRMs, ERPs, payment gateways, analytics platforms and AI services. Each integration deserves to be treated as a governed relationship with its own access rules.
The Pillars That Keep Security Manageable as You Grow
Modular architecture. Monoliths are not evil and microservices are not automatically better. Separation is what matters. When authentication, payments and user data sit in clearly bounded services, a problem in one area does not become a problem everywhere. Modular systems are also cheaper to patch, because a component can be updated without redeploying the whole product.
Cloud native development. Containers, managed services and infrastructure as code turn security into something repeatable. Configuration stops being tribal knowledge held by one engineer and becomes a version-controlled file that can be reviewed, tested and rolled back.
Data driven decision making. You cannot secure what you cannot see. Logging, monitoring and anomaly alerting give teams evidence instead of opinions. The same telemetry that shows where users drop off often shows where something is being probed.
Automation and AI readiness. Automated testing, dependency scanning and continuous deployment catch known issues before release. Preparing for AI adds one more requirement: clean data boundaries, so intelligent features can be introduced later without reaching information they were never meant to touch.
Where Businesses Usually Go Wrong
A short term development mindset. Apps commissioned to hit a launch date rather than serve a five-year plan accumulate shortcuts. Those shortcuts are rarely documented, and they surface during the first serious audit.
Ignoring scale until it hurts. Scalability is inexpensive to plan and expensive to retrofit. How you will handle ten times the traffic is a design conversation early and a rescue operation later.
Choosing the wrong technology stack. Stacks are often selected for speed or familiarity, then inherited by a team that cannot maintain them. Weigh the hiring market, the update cadence of the frameworks and the vendor’s long-term support before committing.
What Good Practice Looks Like
Plan before you build. Give real time to architecture, data flow, compliance requirements and integration mapping. A few weeks of planning routinely saves quarters of rework.
Choose a partner, not a vendor. A capable development partner asks uncomfortable questions about growth, ownership and what happens after launch. Look for teams that discuss maintenance and documentation as readily as features.
Treat optimization as ongoing. Security is a schedule, not a milestone. Dependency updates, penetration testing, access reviews and performance tuning belong in the operating calendar.
A Practical Example
Consider a mid-sized US logistics company whose driver app began as a simple job list. Over four years it absorbed proof-of-delivery photos, customer messaging and route data, all in one codebase with a single shared credential model. When a large retail client made a security review a condition of contract, the assessment stalled.
Instead of patching, the company separated authentication, media handling and dispatch into distinct services, moved to a managed cloud environment and introduced automated dependency scanning. The review passed on the second attempt and the contract closed. The same architecture later supported an AI-assisted route optimization feature that would have been impractical in the original build. The work paid for itself twice, once in reduced risk and once in revenue.
This is the kind of outcome that firms such as NewAgeSysIT work toward with growing businesses. NewAgeSysIT is a software development company in New Jersey serving clients primarily across the United States, with delivery teams focused on mobile, web and AI-enabled systems. Its engineering approach leans on architecture reviews and long-term maintainability rather than one-off delivery, which is precisely where mobile security problems are either prevented or created.
The Long View
Mobile apps are harder to secure today because they carry more responsibility than they were built to hold. The answer is not more tools bolted onto a fragile base. It is a deliberate architecture that expects growth, treats integrations as governed relationships, and makes security a routine part of operating the product.
Businesses that invest at that level rarely talk about their apps in terms of incidents avoided. They talk about contracts won, markets entered and features shipped without drama. That is what well-architected software actually buys you.

Privacy used to be a checkbox buried in a footer link. Nobody read it. Today, it’s a core part of how people decide whether to trust a product at all. A confusing consent screen or a vague data policy can cost a business real users, not just goodwill.
Good privacy design isn’t only about encryption or legal compliance. It’s about how information is presented, how choices are framed, and whether the interface respects the person using it. Below is a practical look at what that actually means for teams building security-focused web applications.
Why Privacy Has Become a Design Requirement
Surveys consistently show that most internet users worry about how their data is collected and used. One widely cited Pew Research study found that roughly 67% of Americans are concerned about how companies handle their personal information, and a similar share feel they have little control over it. That’s not a niche anxiety anymore. It’s mainstream.
For designers, this changes the brief. Privacy can no longer sit at the bottom of the priority list, addressed only after the “real” features are done. It has to shape decisions from the first wireframe, because users are actively looking for signals that a product takes their data seriously.
Build Data Minimization Into Every Screen
The simplest privacy principle is also the easiest to ignore: don’t ask for what you don’t need. Every extra form field, every optional-but-requested phone number, every “just in case” data point adds friction and raises suspicion. Fewer fields usually mean higher conversion, too, so this isn’t purely an ethics argument.
Designers should treat each data request as a cost. Ask: does this feature genuinely require this information right now, or could it be requested later, only when it’s actually necessary? Progressive disclosure — collecting data gradually as trust builds — tends to work better than front-loading a long signup form.
Give Users Real Control Over Their Own Connection
Server-side protection only covers half the picture. Applications that take privacy seriously also point users toward tools that secure their connection, especially on public networks. This is one reason many security-conscious platforms now recommend pairing account-level protections with a dedicated VPN. One of the significant advantages of this type of service is its support for all platforms, offering applications for Windows, smart TVs, and browser extensions. You can visit this site to see how mobile integration works in practice. This doesn’t eliminate the need for server-side efforts, but it helps protect against potential leaks and the emergence of hidden spots where it’s impossible to monitor and ensure security.
That kind of guidance matters more than it might seem. A person connecting from an airport Wi-Fi network is far more exposed than one on a home router, and most interfaces never mention this at all.
Make Consent Requests Honest
Pre-checked boxes, tiny “reject all” links, and consent banners designed to be annoying until you click “accept everything” are dark patterns. They might boost short-term metrics. They also erode trust fast, and regulators in several regions are increasingly penalizing them.
A better approach treats consent as a real choice, not an obstacle course:
- Present “accept” and “reject” options with equal visual weight
- Explain, in plain language, what each data category is used for
- Avoid pre-selecting anything the user hasn’t actively chosen
- Make it just as easy to withdraw consent later as it was to give it
None of this is complicated. It just requires resisting the temptation to nudge users toward “yes.”
Use Visual Signals Users Actually Trust
Lock icons, “secure” badges, and https indicators became so common that many users stopped noticing them. What tends to work better now is specific, plain-language reassurance placed exactly where anxiety spikes — right before a payment field, for instance, or next to a request for a government ID.
Instead of a generic shield icon, a short sentence like “We never store your card number” does more work. Specificity builds credibility. Vague symbols, no matter how polished, don’t.
Avoid Dark Patterns in Privacy Settings
Privacy settings buried three menus deep, toggles that reset after every update, or wording so ambiguous nobody’s sure what they’re agreeing to — these all count as failures, even if the backend is technically compliant. As one UX researcher put it during a recent industry panel, “Privacy that users can’t find is privacy that doesn’t exist for them.”
Settings should be searchable, grouped logically, and described in short, direct sentences. If a setting affects data sharing with third parties, say so explicitly rather than hiding it behind generic phrasing like “personalization preferences.”
Small Interface Details That Build Confidence
Sometimes trust comes down to details that seem minor. A visible last-login timestamp. A one-click way to download or delete all stored data. Even the tools a company recommends can signal how seriously it treats privacy. Pointing users to a lightweight option like the Chrome extension, for example, shows that browsing protection is something the product actively cares about, not just a checkbox in the privacy policy. Security is something that builds from small bricks and grows into an impenetrable wall.
These small additions rarely show up in a feature list, but they’re often what users remember when deciding whether to keep using an app or delete their account entirely.
Test With Real Users, Not Just Compliance Checklists
Legal review confirms a product meets regulatory requirements. It doesn’t confirm that a real person understands what they’re agreeing to. Usability testing focused specifically on privacy flows — consent screens, data export tools, account deletion — often reveals confusion that a compliance audit would never catch.
Even a handful of five-person test sessions can expose where language is unclear or where a “delete my account” button quietly doesn’t delete everything. That gap between legal compliance and actual user understanding is where most privacy-related frustration lives.
Final Thoughts
Privacy-focused UX isn’t a single feature you bolt onto a finished product. It’s a set of small, consistent decisions: what you ask for, how you phrase consent, what tools you recommend, and how honestly you present risk. None of these choices are flashy. Together, though, they’re often what separates a product users trust from one they quietly abandon.
AI-assisted development can help teams turn ideas into working code quickly, but speed does not remove the need for engineering judgment. An AI coding assistant can draft functions, tests, integrations, and documentation, yet the team that approves a change remains responsible for its behavior in production.
The safest approach is to treat generated output as an implementation draft, not as proof that a feature is correct. Code can be neatly formatted, include confident comments, and pass a narrow test suite while still misunderstanding business rules, mishandling data, or failing under realistic conditions.
Why AI-Generated Code Needs a Different Review Process
Generated code can arrive much faster than a reviewer can fully evaluate it. It may follow common patterns without understanding the product’s specific rules, such as which customers are eligible for a refund, when an account should be locked, or what data must never be logged. Reviewers must therefore examine both what the code does and what assumptions it makes.
Security deserves particular attention because generated code may introduce unsafe input handling, excessive permissions, or risky integration patterns. Teams can use the most critical web application security risks as a practical reference when checking changes that process requests, access accounts, query databases, or expose APIs.
Start With the Purpose of the Change
Before reading individual lines, confirm the intended outcome. Read the task description, identify the user problem, and compare the changed behavior with the original request. Look for unrelated file edits, additional services, or new dependencies that are not needed.
For example, a request to add a checkout discount field should not quietly alter payment capture logic, customer roles, or account permissions. A feature can appear to work while changing a critical workflow outside its approved scope.
Check the Code for Logical Errors
Review conditions, loops, return values, and error paths with the application’s real rules in mind. Ask whether the implementation works only for the example described in a prompt or whether it also handles missing records, duplicate requests, invalid types, and partial failures.
Compare the change with nearby, established functions. Inconsistencies in validation, authorization, date handling, or status values often reveal an incorrect assumption. Pay close attention to code that silently falls back to a default value, because a quiet failure can be harder to detect than an explicit error.
Test More Than the Happy Path
Generated tests often demonstrate that the expected input produces an expected result. Production systems also need safe behavior when requests are incomplete, services are unavailable, or two users act simultaneously.
Useful Test Cases to Add
- Blank forms, missing fields, and malformed requests
- Very large inputs, unusual characters, and invalid dates or prices
- Expired sessions, missing permissions, and unauthorized access attempts
- Repeated submissions, duplicate events, and race conditions
- Network timeouts, failed third-party calls, and unexpected database responses
Test the desired outcome, then test the safest failure response. A checkout process, for instance, should not create duplicate orders when a payment provider times out after receiving a request.
Review Security Before Functionality
Search the change for hard-coded passwords, API keys, tokens, private URLs, and debug output containing sensitive information. Confirm that user input is validated, database operations use safe query patterns, and error messages do not reveal internal details.
Inspect authentication and authorization separately. Authentication answers who a user is, while authorization determines what that user may do. Also review file access, shell commands, outbound requests, and permissions granted to integrations. Secure development practices should be built into the workflow, not reserved for a final release check, consistent with the secure software development framework maintained by NIST.
Inspect Dependencies and Third-Party Packages
List every package introduced by the change and ask why it is necessary. Verify the exact package name, avoid lookalike libraries, use approved versions, and retain lockfiles to ensure builds are repeatable. Automated dependency scanning is helpful, but it does not replace the need to review whether a package requires access to sensitive data, the file system, or network resources.
Review Data Handling and Privacy
Identify what the feature collects, stores, transmits, and logs. Remove personal or confidential information from debugging output, protect sensitive data during transfer and storage, and verify that retention behavior matches the product’s needs. For health, financial, education, employment, or similarly sensitive information, involve the appropriate privacy, legal, or security stakeholders before release.
Look for Performance and Reliability Problems
Check for database queries inside loops, unbounded result sets, large files loaded entirely into memory, and external calls without timeouts. Confirm that retries have limits and backoff, and ensure caching cannot expose private or stale data. A report that performs well with 20 records may become unusable when asked to process 200,000 records, so test with realistic data sizes and expected traffic.
Make the Code Easy to Maintain
Working code becomes expensive when future developers cannot safely understand it. Prefer clear names, focused functions, consistent project conventions, and comments that explain decisions or constraints. Break apart oversized generated functions, remove duplicated logic where a shared component is safer, and document unusual behavior that another reviewer might otherwise mistake for a bug.
Use a Layered Review Workflow
- Scope check: Confirm that the change matches the approved request.
- Logic check: Review business rules, edge cases, and failure paths.
- Security check: Inspect inputs, permissions, secrets, data, and dependencies.
- Test check: Run automated tests and add cases that the generated suite missed.
- Release check: Deploy gradually, monitor behavior, and prepare a rollback path.
Keep Pull Requests Small and Traceable
Ask for one feature or fix per pull request whenever possible. Require a short summary of the intended behavior, notable generated sections, manual edits, tests run, and operational risks. Small changes help reviewers identify unintended effects, while feature flags and staged deployment provide extra protection for important user flows.
Questions Reviewers Should Ask
- What problem does this code solve, and what assumptions does it make?
- What happens when input is missing, invalid, duplicated, or delayed?
- Can anyone access data or take actions they should not have access to?
- Which packages, services, permissions, or data flows are new?
- How will the team detect failure, and how will it roll back safely?
Conclusion: Speed Works Best With Strong Verification
AI-generated code can accelerate delivery, but it should earn its way into production through careful review. Clear requirements, focused pull requests, meaningful tests, security checks, maintainable design, and accountable human approval enable teams to gain speed without sacrificing reliability or control.
-
 NEWS1 year ago
Historical Churches in Manila
-
 TOPIC2 months ago
Unveiling AvTub: Your Ultimate Guide to the Best AV Content
-
 TOPIC1 year ago
Symbols of Hope: The 15th Belenismo sa Tarlac
-
 TOPIC1 year ago
RIZAL at 160: a Filipino Feat in Britain
-
 TOPIC1 year ago
“The Journey Beyond Fashion” – Ditta Sandico
-
 TOPIC3 weeks ago
Understanding Fascisterne: Origins and Ideological Roots
-
 TOPIC1 year ago
Simbang Gabi and Kakanin
-
 TOPIC1 year ago
5 Must-Have Products From Adarna House to Nurture Your Roots