TECHNOLOGY
How to Consolidate IT Compliance Across HIPAA, PCI, CMMC, and NIST

Introduction
Managing several compliance requirements at once can quickly become a full-time job for an already stretched IT department. HIPAA, PCI DSS, CMMC, and NIST each have their own language and requirements, but many of the underlying security practices overlap. Treating every framework as a completely separate project can lead to duplicated work, scattered documentation, and unnecessary technology costs.
The problem becomes especially noticeable when audit preparation takes priority over actual security improvements. Instead of spending time strengthening systems, IT staff may find themselves collecting screenshots, updating spreadsheets, and searching for evidence that was already provided for another assessment.
A better approach is to build security controls that address multiple requirements at once. By organizing compliance around the controls themselves rather than individual frameworks, organizations can create a stronger security foundation while reducing the administrative burden associated with audits.
The Multi-Framework Trap
The “multi-framework trap” happens when an organization manages each compliance requirement as an isolated program. A team may maintain one set of documentation for HIPAA, another for PCI DSS, and separate evidence for CMMC and NIST. Although the frameworks are different, many of the same security practices appear throughout them.
This creates unnecessary repetition. An IT team might have to demonstrate how it manages user access for one audit, then collect similar evidence again for another. The same can happen with encryption, endpoint security, vulnerability management, logging, and incident response.
The problem is not simply the number of frameworks. It is the way organizations approach them.
When every audit becomes a separate project, compliance can consume valuable IT resources without necessarily improving the company’s security posture. Teams spend time preparing for assessments instead of addressing vulnerabilities, improving infrastructure, or supporting broader business objectives.
The answer is not to ignore individual framework requirements. Instead, organizations should identify where those requirements overlap and build a common security foundation that can support multiple standards.
Moving From Framework-First to Control-First Security
A framework-first approach starts with the checklist. IT teams review each requirement, determine what needs to be documented, and then move on to the next framework.
A control-first approach starts with the organization’s security needs. The team identifies essential safeguards, implements them consistently, and then maps those controls to the requirements of the applicable frameworks.
This distinction can make compliance much easier to manage.
Consider multi-factor authentication. MFA may be relevant to HIPAA, PCI DSS, CMMC, and NIST requirements. Rather than treating MFA as four separate compliance tasks, an organization can implement a single effective MFA policy and document how that control satisfies the applicable requirements.
The same principle applies to endpoint protection, encryption, access management, vulnerability scanning, and security logging. A well-designed control can support multiple compliance objectives without requiring separate systems for each one.
This approach also produces a more useful security program. Instead of asking, “What do we need to do for this audit?” the IT team can ask, “What controls do we need to keep our environment secure, and which requirements do those controls address?”
Crosswalking Controls Across HIPAA, PCI, CMMC, and NIST
Crosswalking is one of the most practical ways to put a control-first strategy into action. It involves mapping individual security controls to the requirements they address across different frameworks.
For example, an organization might use centralized identity management and MFA throughout its environment. That same implementation can potentially provide evidence for several compliance requirements, provided the control is configured and documented appropriately.
Common areas of overlap include:
| Security Control | HIPAA Security Rule | PCI DSS | CMMC | NIST SP 800-171 |
| Multi-Factor Authentication | Authentication controls | Authentication requirements | Access Control | Identification and Authentication |
| Data Encryption | Encryption requirements | Protection of stored data | System and Communications Protection | System and Communications Protection |
| Endpoint Protection | Malware protection | Malware prevention | System and Information Integrity | System and Information Integrity |
| Audit Logging | Audit controls | Logging and monitoring | Audit and Accountability | Audit and Accountability |
The exact applicability of each requirement depends on the organization’s environment, scope, and compliance obligations. Crosswalking should therefore be treated as a planning tool, not as a claim that one control automatically satisfies every requirement.
Still, the benefits are significant. A centralized security stack can reduce redundant software purchases, simplify evidence collection, and give IT teams a consistent way to monitor important controls.
For organizations that need help designing and maintaining this kind of environment, managed IT services in Denver can provide ongoing technical support while helping keep security controls aligned with business and compliance requirements.
The Hidden Risk of Compliance Drift
Implementing the right controls is only part of the process. Those controls have to remain effective after the audit is over.
This is where compliance drift becomes a serious concern.
IT environments change constantly. Employees join and leave the organization. New applications are introduced. Firewall rules are modified. Servers are replaced, and cloud resources are created. A configuration that was compliant six months ago may no longer meet the organization’s security requirements today.
For example, an administrator might temporarily open a firewall port to troubleshoot an application and forget to close it afterward. A new employee might receive broader permissions than necessary. A newly deployed server might not receive the same security configuration as existing systems.
None of these changes necessarily looks like a major problem in isolation. Over time, however, small gaps can create significant exposure.
Annual audits cannot solve this problem by themselves. An assessment provides a snapshot of the environment at a particular point in time. Continuous monitoring is needed to identify changes between assessments.
Automated configuration checks, vulnerability scanning, patch management, access reviews, and centralized logging can help organizations detect problems much sooner. Instead of discovering a security gap during the next audit, IT teams can address it while it is still manageable.
Making Compliance Part of Everyday IT Operations
Compliance works best when it becomes part of normal IT operations rather than a separate activity that happens once or twice a year.
Routine processes such as patch management, backup verification, access reviews, endpoint monitoring, and vulnerability assessments can support both security and compliance. When these activities are performed consistently, gathering audit evidence becomes much easier because the necessary information already exists.
A practical approach can be organized into four stages:
Stabilize: Review the current environment, identify overlapping requirements, and establish a baseline of essential controls such as MFA, endpoint protection, secure configurations, and reliable backups.
Secure: Strengthen the environment with layered security, network segmentation, least-privilege access, vulnerability management, and continuous monitoring.
Optimize: Remove redundant tools, automate routine processes, and centralize documentation and reporting wherever practical.
Strategize: Review the security program regularly and adjust it as the business, technology environment, and regulatory requirements change.
This approach also makes it easier for internal IT teams to focus on higher-value work. Instead of repeatedly preparing evidence from scratch, they can rely on established processes and centralized systems that continuously generate useful security information.
Organizations that do not have enough internal resources to maintain these processes can also work with an experienced IT services provider. The right partner can help monitor infrastructure, manage security controls, document processes, and identify gaps before they become larger compliance problems.
Building a More Sustainable Compliance Strategy
The goal of compliance should not be to create the largest possible collection of policies and spreadsheets. It should be to establish a secure, repeatable environment where important controls are consistently applied.
That means looking for opportunities to consolidate technology, standardize security practices, and automate evidence collection. It also means recognizing that compliance requirements will continue to evolve. A system designed around one audit cycle may quickly become outdated if the underlying security processes are not maintained.
A control-first strategy provides greater flexibility. When new requirements appear, organizations can evaluate their existing controls and determine what needs to change instead of rebuilding the entire compliance program from scratch.
More importantly, this approach connects compliance to actual risk management. Strong access controls, reliable backups, effective endpoint protection, and continuous monitoring are valuable even when no auditor is involved.
Conclusion
Managing HIPAA, PCI DSS, CMMC, and NIST requirements does not have to mean maintaining four completely separate compliance programs. While each framework has its own requirements and scope, organizations can often reduce duplication by identifying common security controls and mapping them across applicable standards.
A control-first strategy provides a practical foundation for doing this. Crosswalking allows teams to connect existing safeguards with multiple requirements, while continuous monitoring helps prevent compliance drift between audits.
The bigger benefit is that compliance becomes part of everyday IT management. Patching systems, reviewing access, monitoring endpoints, testing backups, and maintaining secure configurations all contribute to both cybersecurity and regulatory readiness.
Organizations that move away from last-minute audit preparation can spend less time chasing documentation and more time improving the systems that protect their data. The result is a compliance strategy that is easier to maintain, more closely connected to real security needs, and better suited to a constantly changing IT environment.

If you typed fentomagazine.com USA into a search bar, you are probably trying to answer a simple question. Is this an American magazine, a U.S. edition, or just the main website seen from an American search? The short answer is the last of those. Fentomagazine.com is the public site for Fento Magazine. The “USA” part of the query usually reflects location-based search intent, not a separate branded American edition sitting in the main menu.
That distinction matters before you judge the content, the tools, or the legal pages. A New York governing-law clause is not the same thing as a newsroom on a Manhattan floor. Readers in the United States can still open the site, browse articles, and use the social-media sections without a subscription. What they should not assume is a dedicated U.S. masthead that the public navigation does not currently show.
Quick answer for featured snippets
Fentomagazine.com USA is best read as a search phrase for Fento Magazine and its usefulness to readers in the United States. The publication’s own About page frames the brand around words, comments, opinions, and online conversations. The live site also publishes broader general-interest pieces and hosts caption and bio resources.
| Question | Plain answer |
|---|---|
| What site is it? | FentoMagazine.com, the main Fento Magazine website |
| Separate USA edition? | Not shown in current public navigation |
| U.S. legal note | Terms and privacy policies reference New York law |
| Core theme | Comments, opinions, and digital conversations |
| Extra sections | Instagram captions, bios, and a captions generator |
| Access | Public browsing, no paywall required to read |
What Fento Magazine says it covers
Fento Magazine describes itself as a place that treats comments as more than noise. On its About page, the publication says words carry weight, and that comments, opinions, and feedback shape how people see news, entertainment, culture, and each other. The stated vision is to decode public discussion rather than only repeat what someone posted.
That original brief still explains the site’s personality. Coverage interests listed by the publication include social-media reactions, celebrity and influencer commentary, news opinions, pop culture, internet trends, memes, and everyday online arguments. In practice, the homepage has also carried pieces on business, technology, home improvement, and other general topics. So the brand story and the current article mix are related, but they are not identical.
For a U.S. reader, that mix can be useful in two ways. First, you can treat the site as a casual reading destination. Second, you can use the caption and comment sections when you need wording ideas for a post. Neither use replaces a primary source when the topic is legal, medical, or financial.
Is fentomagazine.com USA a separate edition?
This is the point most people get wrong. A country name in a search does not always mean a country edition exists. Based on the site’s public structure, Fento Magazine runs through one main domain. There is no clearly labeled USA portal in the main navigation that would function like a standalone American magazine.
There is a separate legal detail. Public summaries of the Terms of Service and Privacy Policy note that New York, United States, is the stated governing jurisdiction, with disputes directed to New York courts. That is a contract clause. It tells you which law the site says applies to its terms. It does not, by itself, prove a physical headquarters, a U.S. newsroom, or a separately edited American issue.
Keep those two facts in different boxes:
- Confirmed from public pages: one main website, plus a New York law reference in the legal policies.
- Not established by those pages: a distinct Fento Magazine USA edition or a verified street address.
If you need an official location for a business filing or a press contact, use the Contact page and ask. Do not infer an office from a jurisdiction sentence.
How the site is organized
Navigation is straightforward. Visitors typically see Home, Comments, Instagram Captions, Instagram Bio, a Captions Generator, and Contact. Standard trust pages sit alongside those sections, including Privacy Policy, Terms of Service, Disclaimer, and About Us. The site is a WordPress-based publication, which is common for independent digital magazines.
Guest-post pitches are invited through the contact channel rather than through an open upload form on the homepage. That is normal. It also means acceptance is not guaranteed, and a published byline should not be treated as staff reporting unless the page says so.
| Section | What a reader can do with it |
|---|---|
| Comments | Read pieces built around reactions and public opinion |
| Instagram Captions | Browse caption ideas for posts and stories |
| Instagram Bio | Look at short bio lines and profile wording |
| Captions Generator | Produce draft caption options to edit |
| Contact | Send a question or a guest-post pitch |
| About and legal pages | Check the brand story, terms, and privacy notes |
Social tools versus editorial articles
The caption sections are the most practical part of the site for many visitors. A caption generator can save a blank-page moment. It will not know your brand voice, your audience, or the claim you should not make. Treat the output as a draft. Rewrite the line so it matches the photo, drop anything you cannot stand behind, and avoid copying a caption that already belongs to another creator.
The article side is wider. Recent public coverage has ranged across business, technology, law-related explainers, home topics, and digital culture. That breadth helps discovery. It also means quality can vary by page. A caption list and a piece on a technical subject should not be read with the same level of trust. Check dates, look for sources, and cross-check anything you might act on.
Who the site is actually for
Fentomagazine.com USA searches tend to come from a few groups.
Students and casual readers want a quick definition of the brand. Social managers want caption and bio prompts. Bloggers want to know whether guest posts are accepted. Skeptical visitors want to know if the domain is a real site or a thin doorway page.
On the legitimacy question, the honest split is this. The domain is a functioning website with ordinary informational pages. Browsing does not require you to hand over payment details. That is enough to call it a real publication in the basic sense. It is not enough to call every article an authority source. Independent sites earn trust page by page.
Pros and cons
Pros
- Free to browse, with no account required for ordinary reading.
- Clear sections for captions, bios, and comments.
- A stated editorial angle around conversation and public reaction.
- Contact path for questions and guest-post pitches.
- Legal pages are present, which many thin sites skip.
Cons
- No separate USA edition is identified in public navigation, so the keyword can mislead.
- Topic range is broad, so depth is uneven.
- Generator output still needs human editing.
- New York jurisdiction language is easy to overread as a headquarters claim.
- Individual articles should be checked before you rely on them.
Common mistakes
People repeat the same errors when they land on this keyword.
They treat “USA” as proof of an American edition. They quote the New York clause as if it were an office address. They paste generator captions without editing. They assume a guest post will publish because the contact page exists. They also use a general article as the only source for a decision that needs a primary document, a licensed professional, or a current official page.
Another miss is ignoring the date. Digital magazines update menus and categories. A review from last season may not match today’s homepage. Open the live site before you cite a feature.
Best practices for U.S. readers
Start with the About page so you know the brand claim. Then open the section that matches your job, whether that is captions or a topic article. If you use the generator, rewrite every line and remove claims you cannot verify.
When you evaluate an article, use a short checklist:
- Does the page name sources, or only opinions?
- Is the date visible?
- Does the disclaimer limit how the content should be used?
- Would you still trust the claim after checking one outside source?
For guest pitches, send a specific idea, a short sample, and a clear note on whether the piece is original. Do not submit the same draft to several sites at once if one of them asks for exclusive use.
How fentomagazine.com USA compares with a typical digital magazine
Traditional magazines often split by country edition, with separate editors and ad teams. Fento Magazine, on current public evidence, does not present that split. It behaves more like a single-domain digital publication with a conversation theme and a set of social-writing tools.
| Point of comparison | Typical country edition | Fentomagazine.com as it appears now |
|---|---|---|
| Branding | Clear USA or regional masthead | Main Fento Magazine brand |
| Domain | Often a country path or sister site | Primary fentomagazine.com domain |
| Legal note | Varies by publisher | New York law referenced in policies |
| Content mix | Usually a defined beat | Comments plus broad general topics |
| Tools | Rare on legacy titles | Caption and bio resources |
| Reader access | Sometimes metered | Public reading |
That comparison keeps expectations realistic. You are not opening a U.S. newsweekly. You are opening an independent site that U.S. readers can use for light research, wording ideas, and general reading.
Practical examples
A creator in Austin wants five caption options for a product photo. They open the captions area, generate a draft, then rewrite it with the product name, a real detail from the shoot, and a call to action they can honor. The tool saved time. The edit made the line usable.
A reader in Chicago sees a technology article and wants to share it. They check the date, look for a named source, and link the original study if the piece mentions one. The magazine page becomes a starting point, not the final citation.
A freelance writer wants a byline. They use Contact, pitch one unused topic tied to comments or digital culture, and wait for a reply. Silence is an answer. A published post should still disclose sponsored or contributed status if the editor requires it.
Conclusion
Fentomagazine.com USA is a search label more than a separate magazine. The site behind it is Fento Magazine, a public digital publication built around comments and online conversation, with caption tools and a wider set of general articles. U.S. readers can use it freely. They should also read the New York legal clause for what it is, skip the assumption of a USA edition, and judge each page on its own evidence. Used that way, the site is a practical stop for wording ideas and casual reading, not a substitute for primary sources.
FAQs
What is fentomagazine.com USA?
It is a search phrase for Fento Magazine’s main website, usually used by people checking the site from or about the United States. It is not the name of a clearly separate American edition in current public navigation.
Is Fento Magazine a real website?
Yes. Fentomagazine.com is a functioning site with an About page, contact option, and standard legal pages. Being real is not the same as being an authority on every topic it publishes.
Does the site have a USA edition?
Public navigation does not show a separately branded USA edition. The main domain is the publication readers open.
Why do people mention New York?
The site’s terms and privacy policies state that New York law governs those policies. That is a legal jurisdiction note, not proof of a street address or a U.S. newsroom.
Can I use the caption tools for Instagram?
Yes. Treat the results as drafts. Edit them for accuracy, voice, and originality before you post.
AI has really changed how digital images get made. Created, edited, reworked for whatever purpose people need. Stuff that used to take specialized software and real technical skill? And a whole lot of time? AI-assisted tools can handle much of that now. One development people keep talking about is Nano Banana 2.5. It’s linked to newer ways of generating and editing images with AI.
But AI image creation isn’t only about making nice-looking pictures. It’s worth knowing what’s actually going on underneath. How the technology works. How these systems make sense of instructions. And where they realistically fit into everyday creative work.
What Is Nano Banana 2.5?
So what exactly is Nano Banana 2.5? The easiest way to see it is as part of generative AI. These are systems that take written instructions, or other inputs, and turn them into visuals. Modern image models rely on machine learning to do it. They learn how language connects to what we see. Objects, places, styles, lighting, composition. All sorts of visual details.
Picture someone describing a product sitting on a wooden table. They want a certain kind of lighting. Maybe a specific artistic look on top of that. They don’t have to build any of it by hand. The AI reads the description and generates the image. It works off patterns it picked up during training.
It’s useful for editing, too, not just creating. Sometimes a brand-new image isn’t what’s needed. AI-assisted systems can change just certain parts of an existing picture. And they try to keep the important bits the same. The layout, the main subjects, the general feel of it.
How AI Image Generation Works
It all comes back to training. These models learn from enormous collections of images and text. Along the way, the system picks up patterns. Basically, statistical links between descriptions and how things look.
So what happens when someone types in a prompt? The model isn’t digging through some hidden folder of pictures. It’s not looking for an exact match. It reads the instructions and builds the visual from scratch. Using everything it’s learned about how things usually look.
A few things can shape how the image turns out:
- The wording and detail of the prompt
- The requested visual style
- Composition and camera perspective
- Lighting and color descriptions
- Objects and people included in the scene
- Relationships between different elements
- Additional reference images or editing instructions
That’s why prompt writing ends up mattering so much. It’s a huge part of getting good results.
From Text Prompts to More Detailed Instructions
The early image generators regular people used were pretty hit-or-miss. Give them a short or vague prompt, and who knows what came out. Newer systems are trying to do better. They’re built to follow more complicated instructions.
Say a user packs a lot into one request. A character, a location, what they’re wearing. The lighting, the background, even the camera angle. The system has to figure out how all of that fits together. It can’t just read each word in isolation.
That’s a real help for creative projects. People can explain ideas the way they’d normally talk. Plenty of folks know exactly what they want to see. They just don’t have advanced editing skills. Now they can describe the idea anyway. Without having to learn every corner of professional graphics software.
Still, a detailed prompt won’t magically give a perfect result. AI can still get spatial relationships wrong. Or mess up proportions, or text. Or miss a specific visual requirement entirely.
AI-Assisted Image Editing
Image-to-image editing is another big piece of this. Here, nobody starts from a blank canvas. Users bring in an image they already have. Then they just describe what they’d like changed.
That could mean swapping the background. Tweaking the environment a bit. Trying out a different artistic treatment. Or changing one particular object. It speeds up experimenting, since there’s already something to work from.
For designers, marketers, educators, and content creators, that’s a nice relief. It cuts down the repetitive manual work. The kind that piles up when testing different visual ideas.
A human still needs to check the result, though. Even small edits can accidentally affect other parts of an image. So it’s smart to look over the whole thing. Not just the one spot that was supposed to change.
Practical Uses Across Different Industries
This tech is useful for a lot more than fun. Businesses can use AI visuals early, while ideas are still forming. Designers can throw together rough concepts first. Then decide what’s worth detailed production work.
Teachers might use generated illustrations to explain abstract ideas. Publishers can play around with visuals for articles or presentations. Independent creators have plenty of uses for it. Social media concepts, video projects, storyboards. Other kinds of digital content, too.
Architecture and product development can get something out of it as well. Quick visual experiments help there. These AI concepts aren’t meant to replace technical drawings. Or professional photography, for that matter. But they’re a handy way to get an early idea across.
The biggest win is usually how fast things move. Creators don’t have to settle on the first concept. They can try out a bunch of options. Then compare which direction works best.
Understanding the Limitations
Yes, things have improved fast. But AI image generation still has its weak spots. Images can come out with wrong details. Objects might look distorted. Characters don’t always stay consistent. Text can get garbled. And complicated instructions sometimes get read in surprising ways.
Then there’s copyright and ownership. How the law treats AI-made content isn’t the same everywhere. It changes from one jurisdiction to another. It can also depend on how much a person actually contributed. And on the material that went into making the output.
Ethics come into it, too, especially with synthetic media. Some images look real enough to fool people. They could be mistaken for actual photos of real events or real people. So anyone using these tools responsibly should stop and think. About the context, about being transparent. And about what could happen once the image is out there.
The Role of Human Creativity
AI doesn’t replace creative judgment. An image still needs a reason to exist. Someone has to decide what to make and how to polish it. And whether it actually gets the message across. That’s still very much a human job.
Tools like Nano Banana 2.5 are part of a bigger shift. Visual creation is getting easier for everyone. What makes them matter isn’t just that they can generate images. It’s that experimenting with visuals now feels like a conversation. Even for people without much technical training.
As these systems keep growing, humans and machines will probably work together more closely. The best workflows will likely use a bit of both. AI for exploring ideas quickly. And people for the parts that need real care. Accuracy, originality, context, and the final call.
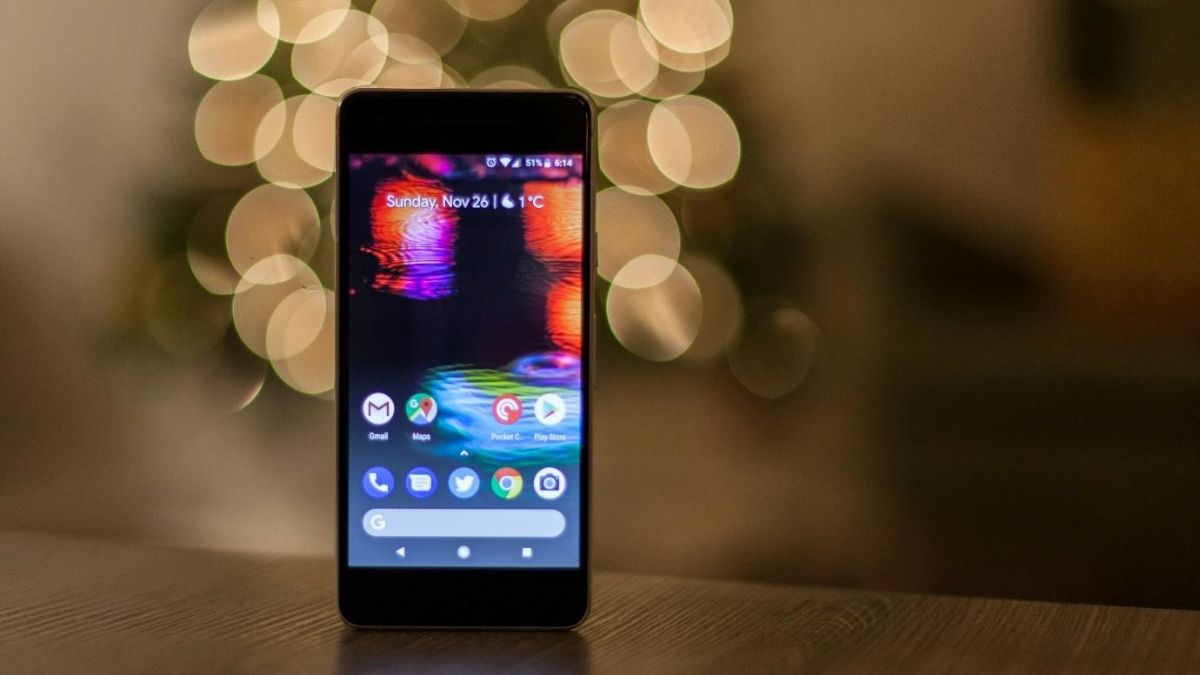
Mobile devices are now common in classrooms, libraries, and other school spaces. Tablets, laptops, and other tools help students complete lessons, research topics, and work with digital content.
Because these devices are used often, they can wear out quickly without proper care. A clear maintenance plan can help schools reduce damage, avoid costly repairs, and keep technology ready for daily learning.
Teach Proper Device Handling
Good maintenance starts with the people using the devices. Students and staff should understand how to carry, charge, clean, and store school technology.
Simple rules can make a big difference. Devices should be carried with both hands, kept away from food and drinks, and placed on stable surfaces.
Protective cases can also help reduce damage from drops and bumps. Screen covers may provide extra protection in classrooms where devices move between students.
Schools can include short training sessions at the start of the year. Clear reminders can help students build better habits over time.
When everyone follows the same rules, devices are more likely to stay in good condition.
Keep Software and Batteries in Good Shape
Software updates are important because they can improve performance and fix security problems. Schools should have a regular process for checking updates on all managed devices.
Battery care also matters. Devices should not stay connected to chargers at all times if the manufacturer recommends a different charging routine.
Extreme heat and cold can also damage batteries. Devices should be stored in safe indoor areas rather than cars, windowsills, or other places with large temperature changes.
Schools that manage many devices may use broader technology solutions for educational facilities to support charging, storage, and device organization.
A consistent system can make it easier for staff to notice battery or software problems before they become serious.
Create a Regular Maintenance Schedule
Waiting until a device stops working can lead to more expensive repairs. A simple schedule helps staff catch small issues earlier.
Weekly checks can focus on cleaning screens, checking chargers, and making sure devices turn on normally.
Monthly checks can include battery condition, storage space, software updates, and physical damage. Staff should also look for loose ports, cracked cases, or charging problems.
At the end of each school term, a larger review can help identify devices that need repair or replacement.
Keeping basic records is useful too. Schools can track which devices have repeated problems and which repairs happen most often.
This information can help with future budgets and purchasing decisions.
Involve the Whole School Community
Device care works better when students, teachers, staff, and families understand their roles.
Teachers can remind students about safe handling during class. Technology staff can manage updates, repairs, and larger maintenance tasks.
Parents may also need clear guidance when devices are taken home. Simple written rules about charging, storage, and reporting damage can prevent confusion.
Students can take part as well. Giving them responsibility for basic checks can help build respect for shared equipment.
The goal should not be to punish every mistake. It should be to create habits that protect school resources and keep devices available for learning.
Conclusion: Build a Smarter Maintenance Routine
Mobile devices can support learning for many years when schools care for them properly.
Teaching safe handling, checking software and batteries, following a maintenance schedule, and involving the school community can all reduce damage.
A strong plan also helps schools spend technology budgets more wisely.
By treating maintenance as part of everyday technology use, schools can keep devices reliable and help students learn with fewer interruptions.
-
 NEWS1 year ago
Historical Churches in Manila
-
 TOPIC3 months ago
Unveiling AvTub: Your Ultimate Guide to the Best AV Content
-
 TOPIC1 year ago
Symbols of Hope: The 15th Belenismo sa Tarlac
-
 TOPIC1 year ago
RIZAL at 160: a Filipino Feat in Britain
-
 TOPIC1 year ago
Simbang Gabi and Kakanin
-
 TOPIC2 months ago
Understanding Fascisterne: Origins and Ideological Roots
-
 TOPIC1 year ago
“The Journey Beyond Fashion” – Ditta Sandico
-
 NEWS4 months ago
What Caused Delta Flight DL275 to Diverted LAX? A Detailed Breakdown