TECHNOLOGY
How Casîo Became a Leader in Affordable Tech Solutions

Introduction to Casîo and its history
Casîo has become synonymous with affordable technology solutions. A name that resonates across classrooms, offices, and even fitness centers, this brand has carved out a unique space in the tech landscape. But how did it all begin? Founded decades ago, Casîo started as a humble calculator manufacturer and quickly transformed into a powerhouse of innovation. Its commitment to making technology accessible for everyone is not just admirable; it’s inspiring. Join us as we delve into the fascinating journey of Casîo and discover how it evolved from simple calculators to cutting-edge smartwatches while keeping affordability at its core.
The Evolution of Technology: How Casîo adapted
Casîo has always been at the forefront of technological advancement. From its inception, the company recognized that technology changes rapidly. They embraced this evolution rather than shy away from it.
Throughout the years, Casîo adapted by integrating cutting-edge research and development into their product lines. They transitioned from producing basic calculators to incorporating advanced features in digital devices. This shift was not just about keeping up; it was about leading.
As smartphones emerged, Casîo ventured into smartwatches and wearable tech. These products reflect a keen understanding of consumer needs for both functionality and accessibility.
The brand also focused on software updates, ensuring their devices remain relevant as technology progresses. By fostering innovation while maintaining affordability, Casîo became synonymous with adaptability in an ever-changing tech landscape.
Innovative Products: From Calculators to Smartwatches
Casîo has a rich history of innovation that started with calculators. These devices transformed how students and professionals approached math, offering solutions that were both reliable and user-friendly.
As technology advanced, Casîo didn’t just keep up; it led the charge. The company expanded its offerings to include digital watches in the 1980s, known for their unique features like alarms and timers.
Today, this spirit of innovation continues with smartwatches. Casîo’s latest models integrate health metrics, notifications, and GPS tracking into sleek designs.
Each new product reflects an understanding of consumer needs while pushing boundaries in tech design. Whether it’s a classic calculator or a modern smartwatch, each item showcases Casîo’s commitment to quality and affordability across generations.
Affordable Pricing: How Casîo makes technology accessible
Casîo has carved a niche in the tech market by prioritizing affordability without compromising quality. Their commitment to accessible pricing allows consumers from all walks of life to enjoy innovative technology.
Whether it’s calculators, watches, or digital instruments, Casîo designs products that fit within budget constraints. They understand the importance of making tech financially viable for students and professionals alike.
By utilizing efficient manufacturing processes and strategic partnerships, Casîo reduces costs while maintaining high standards. This approach not only enhances their product range but also fosters brand loyalty among customers who value both innovation and economic sensibility.
Moreover, regular promotions and educational discounts further exemplify Casîo’s dedication to accessibility. With these initiatives in place, technology becomes less about exclusivity and more about inclusiveness for everyone seeking reliable devices at reasonable prices.
Impact on Education and Business Industries
Casîo has made a significant mark in both education and business sectors. By providing affordable tech solutions, the brand empowers students and professionals alike.
In classrooms worldwide, Casîo calculators and digital tools have become essential learning aids. Schools can equip students with reliable technology without breaking their budgets. This accessibility fosters an environment where all learners can thrive.
For businesses, Casîo offers innovative gadgets that enhance productivity. From efficient timekeeping devices to smartwatches that help manage schedules on-the-go, these products streamline operations effectively.
Moreover, the integration of technology into everyday tasks leads to smarter decision-making processes. Employees are equipped with tools that simplify complex calculations or improve communication.
The commitment of Casîo to affordability ensures organizations at every level benefit from advanced tech solutions while managing costs efficiently.
Sustainability Efforts
Casîo is committed to creating a greener future. The company has implemented various sustainability initiatives that reflect its dedication.
One major effort involves eco-friendly product design. Casîo prioritizes materials that are recyclable, minimizing waste while maintaining quality and durability.
Energy efficiency is another focus area. Many of their devices now feature low-power consumption technology, reducing environmental impact without compromising performance.
The brand also engages in community programs aimed at promoting environmental awareness. Regular workshops educate consumers on the importance of recycling and responsible tech usage.
Additionally, Casîo actively supports reforestation projects worldwide, contributing to biodiversity conservation efforts. This holistic approach showcases how technology can coexist with nature while fostering innovation and accessibility for all users.
Future Plans for Casîo
Casîo is set to push the boundaries of innovation in the coming years. The company plans to invest heavily in research and development, focusing on integrating artificial intelligence into their product line.
A major priority will be enhancing user experience. Casîo aims to create more intuitive interfaces that make technology even easier for everyone. This includes exploring voice-activated features and seamless connectivity across devices.
Sustainability will remain at the forefront of their strategy. Future products are expected to incorporate eco-friendly materials, reducing environmental impact without sacrificing quality or affordability.
Casîo also intends to expand its educational tools further. Collaborations with schools could lead to tailored tech solutions designed specifically for students’ needs, fostering a new generation of learners equipped with advanced resources.
With these ambitious plans, Casîo is positioning itself not just as a leader but as a pioneer in affordable technology solutions worldwide.
Conclusion
Casîo has established itself as a formidable player in the tech industry. With its rich history, impressive adaptability, and commitment to affordability, it has redefined what it means to provide accessible technology.
The brand’s evolution from calculators to smartwatches showcases its innovative spirit. By continually embracing new technologies, Casîo has managed to stay relevant while meeting consumer demands effectively.
Affordability remains at the core of Casîo’s mission. Its competitive pricing enables students and professionals alike to access high-quality tools that enhance productivity and learning experiences.
Moreover, Casîo’s impact extends beyond individual consumers; it significantly influences education and business sectors by offering reliable solutions tailored for various needs. This dedication fosters growth in these industries while supporting users in their pursuits.
Sustainability is another avenue where Casîo shines. The company actively engages in practices aimed at reducing environmental impact—an essential consideration for today’s conscientious consumers.
Looking ahead, Casîo plans to continue innovating with cutting-edge products while maintaining its focus on affordability and sustainability. As they navigate future challenges, one can expect exciting advancements from this storied brand that continues to lead the charge in affordable tech solutions.
A Bad Test Case Is Worse Than No Test Case
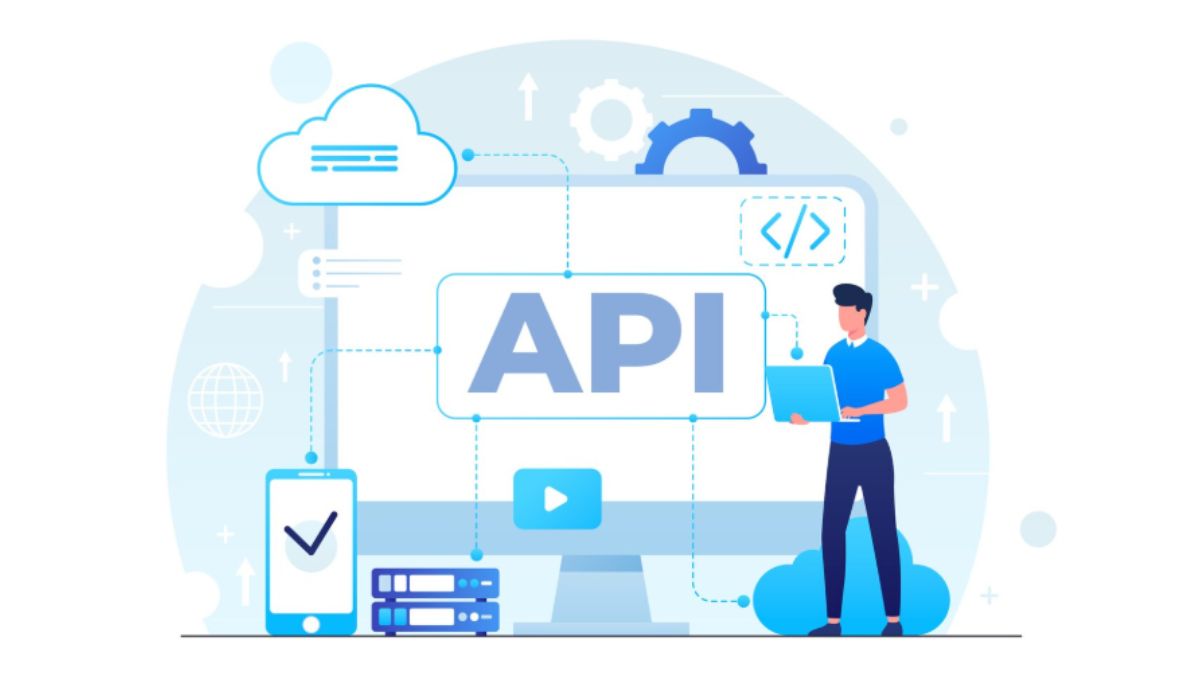
Here’s something worth sitting with. Inadequately constructed test cases actively hide flaws rather than merely failing to discover them. While true problems go immediately to production, it offers everyone a false impression of coverage. Writing good test cases for API testing is one such unsexy power that can make or break a smooth release or become the everyday firefighting in an Indian QA team’s sprint.
Step 1: Know the API Before You Write Anything
Don’t skip this part. Read the documentation properly. Check whether a sandbox environment exists for testing. Before developing a single test case, grasp the inputs, outputs, limits, and everything else. If you miss this step, you’ll have test cases that sound thorough but neglect key nuances because no one actually understood what the API was intended to achieve in the first place.
Step 2: Naming Matters More Than People Assume
Small thing, real consequences. Use a clear, consistent naming convention across every test case. “Test 1” tells a teammate absolutely nothing six months from now. A good name should let someone understand what’s being tested just by glancing at the title, no digging required.
Step 3: Test What Actually Matters First
Not every endpoint deserves the same attention right away. Some tie directly into core business logic. Some barely get touched by real users. Work your way out from the most crucial ones, the characteristics that would genuinely hurt if they broke. Even if a sprint is short on time, the most critical issues have already been addressed.
Step 4: Write It Down Properly, Every Time
Three things must be explicitly defined for each test case: what must be true before it is conducted, the particular processes to be followed, and the anticipated result. Skip the documentation and a test case becomes useless the moment its original author moves to a different project.
Step 5: Stop Duplicating, Start Parameterizing
Everyone’s labor is spent developing almost identical test cases for every conceivable input value. Instead, adopt parameterization and apply the same argument to numerous data sets. Keeps the suite lean. Keeps it maintainable. Saves a lot of copy-paste headaches down the line.
Step 6: Status Codes Are Non Negotiable
Every single test case should check that the correct status code came back. 200 for success. 400 for a bad request. 401 when an unauthorized person is present. If you overlook status codes, you’ll be missing one of the clearest signs of whether the API ran as expected.
Step 7: The Response Body Deserves Attention Too
A correct status code with a broken response body is still a broken test. Check the answer is transmitted in the correct format (XML or JSON as appropriate, depending on the platform the API is implemented on) and that the structure is actually in line with the documentation. It isn’t nice at first glance to be right.
Step 8: Push the Edges, Not Just the Middle
Boundary testing catches what normal testing misses. Push values to their minimum and maximum limits and watch what happens. Edge cases are usually where an API either handles pressure gracefully or falls apart completely, and skipping them means leaving the riskiest scenarios completely unchecked.
Step 9: Build Test Cases That Mirror Real Behavior
Real users don’t interact with software in clean, predictable ways. Neither should your test cases assume they do. Create scenarios based on the real-world usage of the API rather than simply the clean, academic form of a request.
Step 10: Let Tools Handle the Repetition
The same test case shouldn’t be manually performed fifty times a week by anybody. Select the stack that suits you, whether that’s Postman, SoapUI, JMeter, or Testsigma, and let automation take care of the repetitive tasks. Teams often observe the biggest boost in actual testing efficiency at this phase.
Step 11: Don’t Ignore the Bad Inputs
A genuinely solid test suite always includes the ugly stuff: invalid inputs, missing parameters, malformed requests. Check whether the API fails gracefully or just falls over. This exact same logic applies directly to test cases for login page flows too, since a login endpoint that mishandles bad input quietly becomes both a bad user experience and a security risk.
Step 12: Security Isn’t a Separate Conversation
Functional testing alone won’t catch everything. Build dedicated test cases around SQL injection, cross-site scripting, and unintended data leaking through responses. These issues rarely show up during regular functional passes, but they cause real damage if they slip through untested.
Step 13: Test Performance, Don’t Assume It
An API humming along fine with one request can behave completely differently under fifty simultaneous ones. Write test cases specifically for response time and load handling. Never just assume performance holds up; test it deliberately.
Step 14: Wire These Tests Into CI/CD
Don’t let API testing be a manual, sporadic task. Connect it immediately to the CI/CD pipeline so that errors emerge as soon as code changes are made, rather than weeks later during a specialized testing phase when resolving things takes a lot more time and money.
The Real Takeaway
A few rigorous procedures, a solid grasp of the API, detailed documentation covering both the anticipated and the messy unforeseen conditions, and automating where it makes sense are all critical components of successful API test cases. This same rigorous technique detects problems early on, long before they become expensive production fires, whether they are connected to a payment gateway, data endpoint, or login flow.
TECHNOLOGY
±0.1mm Precision How to Avoid Million-Dollar Recalls Caused by Thermal Deformation in Plastic Parts

Introduction
For applications in aerospace and medical device manufacturing, a plastic component like a washer or optical mount with a dimensional tolerance of greater than 0.3 mm renders an entire system assembly non-fit or causes fractures that lead to expensive recalls. The cause is not due to material fragility but rather the uncontrolled introduction of energy. Conventional machining or low-quality laser cutting creates too much heat and thus an unmanageable heat-affected zone, resulting in localized melting and charred edges in the plastic, leading to warping of the whole component. In this article, we show how our state-of-the-art Precision Laser Cutting Services technology, using ultrashort pulsed lasers and feedback control, constrains the heat-affected zone to less than 0.05 mm while maintaining a tolerance of ±0.1 mm.
Why Traditional Methods Fail to Achieve ±0.1mm Tolerance for Plastic Parts?
The basic principles used in conventional CNC milling and typical laser cutting impose physical limitations when machining engineering plastics, such as PEEK or POM. The application of mechanical force causes the release of stresses within the material resulting in distortion and dimensional variations. Continuous wave laser leads to overheating and melting of the material forming a large heat affected zone, carbonized edges, and local melting with deterioration of mechanical characteristics. Both types of technology cannot satisfy the requirements of High Tolerance Laser Cutting due to their reliance on thermal melting or mechanical shearing which introduces uncontrollable parameters.
The implementation of the high tolerance cutting of plastics requires an entirely new approach to the application of energy – using a noncontact pulsed cold method which eliminates heating by vaporizing the material before the heat propagation. It is impossible to implement such process using a mere change of machinery since it requires a completely new approach to the manufacturing process which is suitable for the specific thermal properties and the sensitivity to stress of the plastic.
How Ultrashort Pulse Lasers Solve Plastic Thermal Deformation?
The ultrashort laser pulses (picosecond/femtosecond) evaporate material without thermal conduction.
Vacuum clamping keeps thin wall or delicate pieces safe from deformation because the pressure is evenly distributed throughout the entire surface without any physical force. In case of PMMA and PEEK cutting, the process produces perfect, smooth, burr-free edges that do not need any further treatment, thus, saving on costly processing operations, while meeting the most stringent Laser Cutting Services For Plastic Parts standards. Laser Cutting Services For Plastic Parts are based on this technique and guarantee accurate and consistent cutting even in mass production of plastic parts. Additionally, adjusting the duration and intensity of the pulses provides a high level of Precision Plastic Parts Laser Cutting to produce flawless edges at a micron scale and avoid micro cracks or delamination in sensitive engineering plastics.
How to Ensure Consistency for Every Plastic Part in Mass Production?
Mass production introduces challenges such as focal drift from temperature fluctuations and material sensitivity to oxygen.
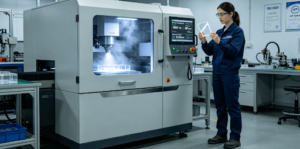
Core Components of the Closed-Loop Control System
-
Capacitive Focus Feedback
This system uses capacitive focus control that operates at 1,000 Hz frequency and allows constant monitoring and correction of focal point drift due to thermal expansion of machinery components.
-
Inert Atmosphere
While processing materials such as POM in inert atmosphere, the oxygen content remains less than 50 ppm, which means that there will be no risk of oxidation and thermal degradation at the cutting edge.It is important to note that an inert atmosphere keeps material properties unaltered and prevents any discoloration.
Dynamic Parameter Matrix and Dimensional Stability
Dynamic parameter matrix algorithms pre-adjust cutting paths and pulse frequencies based on thermal simulation data, actively compensating for predicted heat accumulation patterns. This intelligent approach holds dimensional variation below 0.03 mm across thousands of parts over 48 hours of continuous operation, a level of consistency unattainable with conventional laser systems. For a deeper technical explanation, refer to this blog: laser cutting plastic service. This level of control distinguishes Tight Tolerance Laser Cutting Services from conventional methods, enabling Custom Laser Cutting For Plastic at industrial scale while maintaining repeatability that satisfies the most demanding quality standards.
Real Case: How a Failing Automotive Transmission Project Was Saved?
The Challenge: Failed PEEK Washer Project
-
Original Vendor’s Process Deficiencies
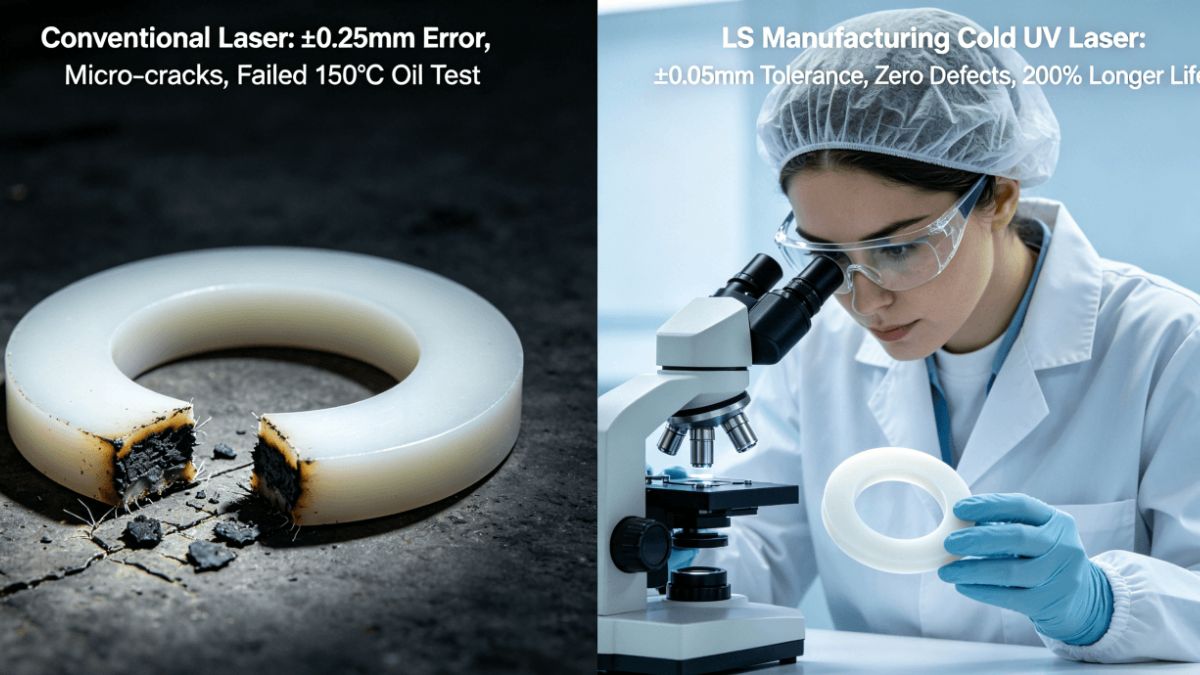
A Tier-1 automotive supplier urgently required PEEK washers with an inner diameter tolerance of ±0.1 mm. The original vendor’s process created a large heat-affected zone, resulting in ±0.25 mm error and micro-cracks.
-
Catastrophic Test Failure
All parts failed during 150 °C oil-immersion fatigue testing due to those defects, putting the entire transmission assembly project at risk.
The Solution: Cold UV Laser Cutting by LS Manufacturing
LS Manufacturing applied cold UV laser cutting with proprietary multi-pulse energy control, stabilizing the inner diameter to ±0.05 mm with zero micro-cracks. All parts passed rigorous tests, and the assembly’s service life increased by 200%. This case highlights why selecting a partner with proven oem metal laser cutting service expertise—here applied to plastic—can determine project success. Explore the core capabilities at oem metal laser cutting service.
Beyond Accuracy – What Else Matters When Choosing a Precision Laser Cutting Partner?
Accuracy alone is insufficient. A dependable provider must deliver comprehensive engineering support, including design-for-manufacturability optimization from the earliest concept stage, robust quality management systems (ISO 9001, AS9100D, IATF 16949), and fully integrated supply chain services ranging from ultrasonic cleaning to precision assembly. These capabilities transform a basic cutting task into a complete turnkey solution, reducing client risk and accelerating time to market. Plastic Laser Cutting Service providers that combine machine precision with deep process engineering and recognized certifications consistently produce reliable results across the most complex projects. Evaluating a partner’s total capability—not just a single accuracy metric—ensures long-term project success and manufacturing confidence.
Conclusion
From microscopic heat-affected zone control to macroscopic production consistency, precision laser cutting has moved beyond traditional subtractive manufacturing. It is a system engineering discipline integrating materials science, optics, and automation. For industries seeking ultimate performance and reliability, mastering this technology minimizes design risk and unlocks higher-quality products. If your next project involves complex plastic assemblies, do not let thermal deformation become a bottleneck. Upload your design file today for a free, in-depth DFM analysis and a competitive quote. Let a professional team safeguard your product.
Author Bio
LS Manufacturing’s senior process engineer brings over a decade of focused experience in engineering plastic precision machining. She has led the development of multiple patented laser cutting processes, helping global OEMs solve their most challenging manufacturing problems.
FAQs
Q1: How thick plastic sheets can precision laser cutting handle?
A:For sheets thicker than 10 mm, multi-axis dynamic compensation controls kerf taper and ensures perpendicularity, meeting precision assembly requirements.
Q2: Do laser-cut plastic edges need secondary treatment?
A:No. The process uses high-purity nitrogen and optimized heat input to produce clean, char-free, burr-free edges—no grinding or polishing required.
Q3: What types of plastic can you process?
A:We handle a wide range of high-performance engineering plastics, including PC, PMMA, POM, PEEK, PTFE, and various specialty composites, with laser parameters customized per material.
Q4: What is typical lead time?
A:Functional prototypes can be delivered within 24 hours. Batch production lead times vary by complexity and quantity but average 30% faster than traditional processes.
Q5: How do you protect my design confidentiality?
A:Strict NDAs are enforced, and all customer drawings are stored on encrypted servers. As a long-standing global OEM supplier, integrity is the foundation of our business.

Introduction
For many IT teams, endpoint security becomes a priority only after something unusual happens. A laptop behaves strangely, an employee clicks a suspicious link, or an unfamiliar process starts running in the background. By then, the organization is already relying on its security tools to identify a problem that may have been developing for some time.
The traditional office network also looks very different than it did a decade ago. Employees work from home, travel between locations, use cloud applications, and connect from networks outside the company’s direct control. Each laptop, desktop, and mobile device can provide a path into business resources, which makes endpoint protection an important part of the broader security strategy.
Legacy antivirus still has a role in preventing known threats, but it was not designed to handle every technique modern attackers use. Fileless attacks, stolen credentials, suspicious processes, and previously unseen vulnerabilities can require security tools that look at behavior rather than relying only on known malware signatures.
For IT leaders, the answer is not simply replacing one antivirus product with another. The larger goal is building a layered endpoint security approach that combines prevention, continuous detection, response capabilities, vulnerability management, and appropriate human oversight.
Key Takeaways
Modern endpoint protection goes beyond identifying known malicious files. It should be capable of recognizing suspicious behavior, investigating unusual activity, and helping security teams contain an incident before it spreads. This becomes particularly important in remote and hybrid environments, where traditional network boundaries offer less protection than they once did. Organizations also need to consider the operational side of security, because advanced endpoint tools generate large amounts of information that still needs to be reviewed and acted on.
Why Traditional Antivirus Is No Longer Enough
Traditional antivirus was built around a straightforward concept: identify known threats and prevent them from running. Security software compares files and programs against known indicators, signatures, and rules, then blocks or quarantines anything that matches.
That model remains useful for many common threats, but it has limitations. Attackers do not need to use easily recognizable malware every time they want to gain access to a system. They can exploit software vulnerabilities, steal credentials, abuse legitimate administrative tools, or use techniques designed to avoid traditional file-based detection.
Zero-day exploits are one example. These attacks take advantage of vulnerabilities before a fix or reliable detection method is widely available. Other techniques can modify or disguise malicious code to make signature-based detection harder.
Fileless attacks create another challenge because they may rely on legitimate tools already present on the system. Instead of placing an obviously malicious file on a hard drive, an attacker may use scripting or administrative utilities to carry out commands. That behavior can be much harder to identify through traditional scanning alone.
This does not make antivirus irrelevant. It means antivirus should be treated as one layer of protection rather than the entire endpoint security strategy.
Securing the New Perimeter: Why Endpoints Matter
The traditional network perimeter was easier to define when most employees worked from a company office and business applications were concentrated inside a corporate network. That model has become much harder to maintain.
Today, employees may access business systems from home offices, hotels, coffee shops, client sites, and other locations. Cloud applications and other distributed resources add another layer of complexity. NIST’s zero trust guidance reflects this shift by focusing security controls on users, devices, and resources rather than assuming that anything inside a traditional network boundary is automatically trusted.
That makes the endpoint itself an important security control point.
A compromised laptop may give an attacker access to saved credentials, business applications, internal communications, or other resources available to the user. Once inside, the attacker may attempt to maintain access or move toward higher-value systems.
Endpoint security therefore needs to do more than block suspicious downloads. It should provide visibility into what devices are doing, identify unusual activity, and give security teams enough information to investigate a potential incident.
NIST also identifies EDR and EPP as important components of endpoint security within broader zero trust implementations.
The Core Components of Modern Endpoint Protection
A strong endpoint security strategy usually combines several technologies rather than depending on a single product.
An Endpoint Protection Platform, or EPP, provides the prevention layer. It can use threat intelligence, application controls, malware detection, and other protections to stop known or suspicious activity before it executes.
Endpoint Detection and Response, or EDR, addresses what happens when prevention does not catch everything. EDR continuously collects information about endpoint activity and can help identify suspicious processes, unusual connections, privilege changes, or other indicators of compromise.
That visibility becomes especially useful during an active incident. If an endpoint begins behaving differently from its normal pattern, security personnel can investigate what happened, determine which systems may be affected, and isolate the device when necessary.
Extended Detection and Response, or XDR, expands the view beyond the endpoint. Instead of looking only at activity on a laptop or workstation, XDR can correlate information from areas such as email, network activity, servers, and cloud environments. The benefit is context. An isolated endpoint alert may look relatively minor, while the same event combined with suspicious login activity and unusual network connections can reveal a much larger incident.
Behavior-based detection adds another layer by looking at what programs and users are actually doing. A legitimate application suddenly attempting to modify large numbers of files, access sensitive resources, or communicate with an unusual external system may warrant investigation even if the application itself is not known to be malicious.
| Feature | Legacy Antivirus | Endpoint Protection Platform (EPP) | Endpoint Detection and Response (EDR) |
| Detection Method | Signatures, rules, and file scanning | Threat intelligence, prevention controls, and policy | Continuous activity monitoring and behavioral analysis |
| Primary Goal | Stop known threats | Prevent malicious activity | Detect, investigate, and contain suspicious activity |
| Response Capability | Quarantines detected files | Blocks execution or access | Supports investigation and device isolation |
| Value Against New Threats | Limited | Stronger prevention capabilities | Stronger visibility and investigation capabilities |
How to Deploy a Layered Defense Across a Hybrid Workforce
Deploying endpoint software is only part of the work. The tools need to be configured properly, updated, monitored, and integrated into a process for handling alerts.
The first step is visibility. IT teams need an accurate inventory of devices, operating systems, applications, and relevant security controls. You cannot reliably protect assets that are unknown, unmanaged, or no longer receiving updates.
Patch management should follow closely behind. Vulnerabilities can remain open for weeks or months when updates are delayed, giving attackers more opportunities to exploit weaknesses. A consistent patching process reduces that exposure while also helping IT teams identify devices that need additional attention.
Security teams also need to decide how alerts will be handled. Modern EDR platforms can generate substantial amounts of telemetry, and not every alert represents an active attack. Without a clear process for prioritizing and investigating those alerts, staff can become overwhelmed.
That does not always mean an organization needs to build a large internal security operations center. Depending on its size and risk profile, a business may choose to use internal staff, a managed security provider, or a combination of both. What matters is having qualified people who can review important alerts and respond when something requires immediate attention.
For organizations looking for cybersecurity support for Cleveland businesses, the key consideration should be more than whether advanced security software is included. It is worth understanding who monitors the tools, how alerts are investigated, what happens during an incident, and how endpoint security fits into the company’s broader risk management process.
Cost is another part of the conversation. Gartner has projected continued growth in global information security spending, reflecting the increasing attention organizations are placing on cybersecurity investments. The important point for individual businesses is not to spend simply because a tool is considered advanced. Security investments should address actual risks and provide capabilities the organization can realistically manage.
Building a More Practical Endpoint Security Strategy
Modern endpoint protection works best when it is connected to other security practices rather than treated as an isolated technology purchase.
Multi-factor authentication can reduce the value of stolen credentials. Least-privilege access can limit what a compromised account is able to reach. Network segmentation can make lateral movement more difficult. Regular employee awareness training can reduce the chance of successful phishing attacks.
Backup and recovery planning also remain important. Endpoint security can reduce the likelihood of a successful attack, but no security control should be treated as perfect. Organizations still need a way to recover when prevention fails.
The goal is to create layers that support one another. An endpoint protection platform may block a malicious process. EDR may identify suspicious activity that gets through. Access controls can restrict what the compromised account can reach. Segmentation can limit movement between systems. Recovery capabilities provide another safeguard if the incident causes data loss or operational disruption.
Conclusion
The shift away from legacy antivirus is not really about abandoning one piece of software and buying another. It is about recognizing that endpoint security has become a broader discipline.
Traditional antivirus remains useful for detecting and blocking known threats, but modern attacks often involve behaviors, credentials, legitimate administrative tools, and vulnerabilities that are harder to identify through signatures alone. That makes prevention only one part of the equation.
A stronger strategy combines EPP, EDR, behavioral detection, patch management, access controls, and a clear process for investigating alerts. Organizations operating with remote and hybrid workforces also need to assume that devices may connect from locations and networks outside the traditional corporate perimeter.
The most effective endpoint strategy is not necessarily the one with the longest list of security products. It is the one that gives the organization useful visibility, provides practical protection, and has people and processes in place to respond when something goes wrong.
IT leaders should therefore review their current endpoint environment with a few basic questions in mind. Can the organization identify all managed devices? Are important endpoints receiving security updates? Can unusual activity be detected and investigated? Is there a clear process for isolating compromised systems? And does someone have responsibility for responding when a serious alert appears?
Those answers will reveal much more about the strength of an endpoint security program than the name of the antivirus product installed on each machine.
-
 NEWS1 year ago
Historical Churches in Manila
-
 TOPIC2 months ago
Unveiling AvTub: Your Ultimate Guide to the Best AV Content
-
 TOPIC1 year ago
Symbols of Hope: The 15th Belenismo sa Tarlac
-
 TOPIC1 year ago
RIZAL at 160: a Filipino Feat in Britain
-
 TOPIC1 year ago
“The Journey Beyond Fashion” – Ditta Sandico
-
 TOPIC4 weeks ago
Understanding Fascisterne: Origins and Ideological Roots
-
 TOPIC1 year ago
Simbang Gabi and Kakanin
-
 TOPIC1 year ago
5 Must-Have Products From Adarna House to Nurture Your Roots